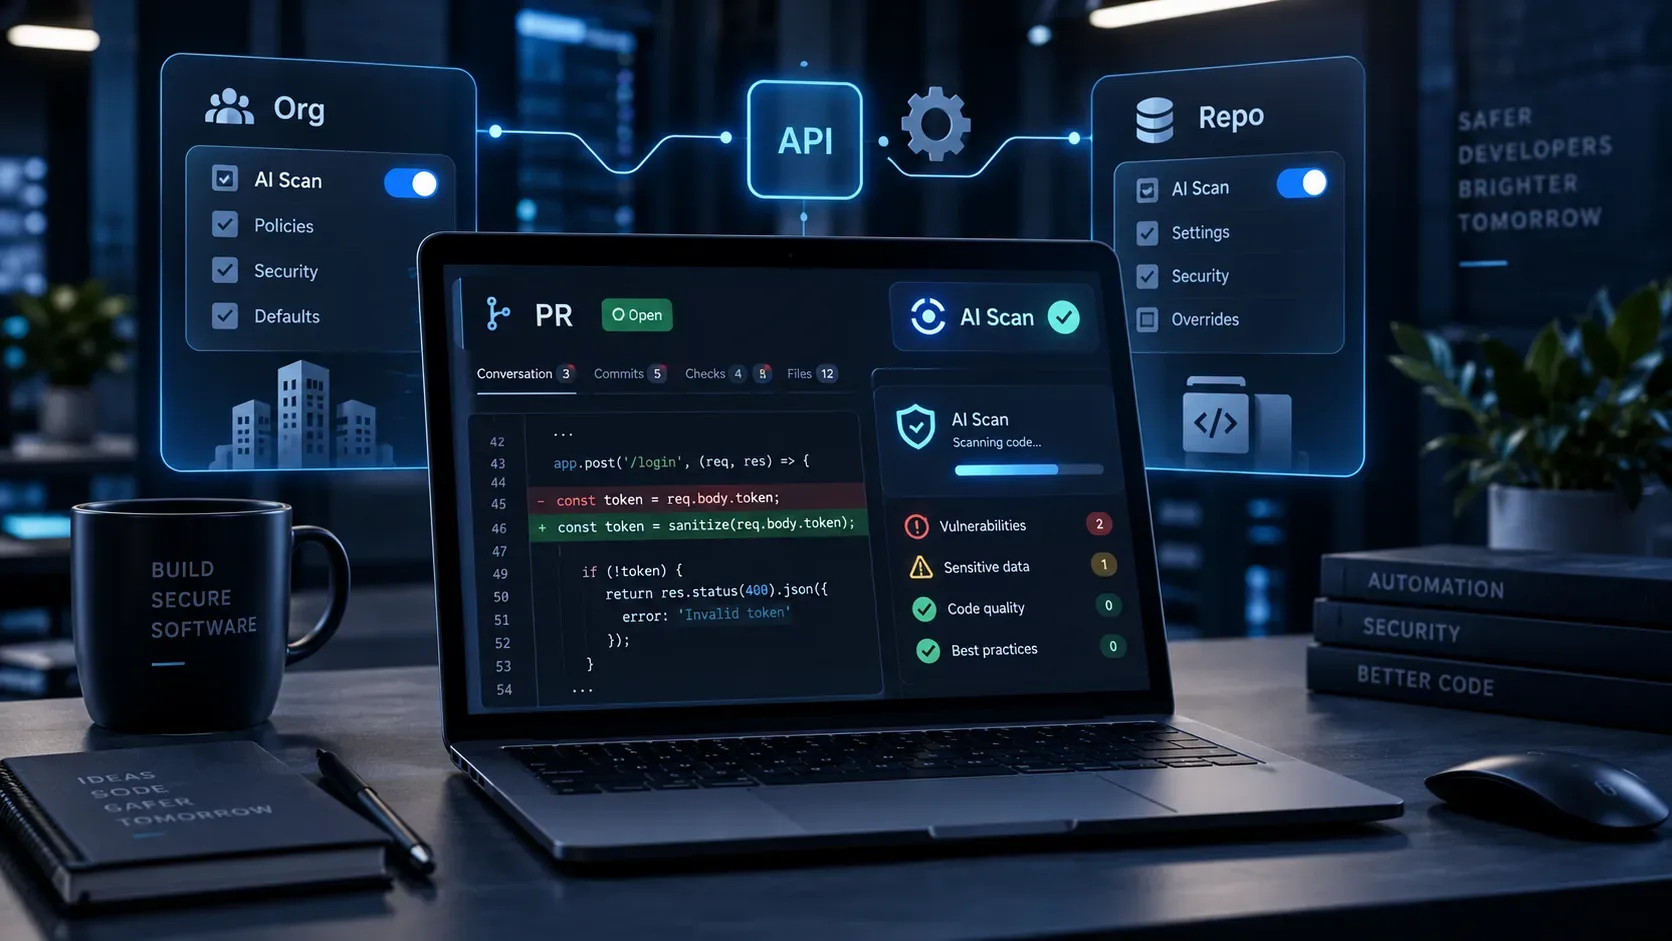
As of September 25, 2026, GitHub's agentic autofix uses Copilot Memory when the feature is enabled. In practice, a remediation session can review existing memories for useful repository context and, after producing a fix, can store the fix pattern as a memory for future use. The potential benefit is that later fixes can better reflect conventions and secure development patterns already observed in the project. For reviewers, however, this adds another layer to the job: in addition to checking the diff, it is useful to consider which persistent context may have influenced the proposal.
What changed in agentic autofix
Agentic autofix already worked as an agent-driven remediation flow. When a code scanning alert is assigned to Copilot, the agent can explore relevant files across the codebase, generate a fix, validate the result, and iterate before opening a pull request for review. The integration announced on September 25 adds Copilot Memory to that cycle for customers who have enabled it.
According to GitHub's changelog, agentic autofix now reviews existing memories for context that may help resolve security alerts. When it creates a fix, it also stores the fix pattern as a memory for later use. GitHub also says these memories can help resolve additional alerts and provide compatible Copilot features, such as code review and the cloud agent, with secure development patterns that are specific to the repository.
Why this changes fix review
Even before this integration, reviewing an automated fix required checking whether the patch actually removed the issue without introducing regressions. With persistent memory, a proposal can also reflect conventions inferred from earlier work. That can improve consistency, but it also makes some reusable context part of future interactions.
For human review, the key point is not to treat a recurring pattern as proof that it is still correct. A fix that worked before may still be inappropriate for a different component, data flow, or trust boundary. GitHub documents that repository-level facts stored by Copilot Memory include citations to supporting code and are revalidated against the current branch before use. This validation helps reduce stale context, but it does not replace pull request review.
What to review in a pull request created by agentic autofix
- Whether the vulnerability is actually remediated: verify the connection between the original alert, its root cause, and the proposed change. Automated validation is useful evidence, but it should be read together with the diff and the reported analysis results.
- Whether the learned pattern fits this context: look for abstractions, helpers, conventions, or architectural decisions that may have been reused. A pattern that is appropriate in one module may be inappropriate in another.
- Whether there are lateral changes: agentic autofix can explore files beyond the initial alert location. Review scope, related calls, configuration, tests, and indirect effects.
- Whether tests cover the relevant behavior: validate success and failure paths, hostile inputs, authorization, error handling, and edge cases that match the vulnerability.
- Whether the fix changes trust boundaries: pay special attention to authentication, authorization, serialization, queries, files, commands, networking, secrets, and input validation.
- Whether the agent's explanation matches the code: do not use the pull request summary as a substitute for reading the patch. The description should match the actual change and the validation results.
Copilot Memory is more than a fix history
Copilot Memory can store repository-level facts, including coding conventions, architecture decisions, build commands, and project-specific rules, as well as user-level preferences. The documentation says supported features can share this knowledge. For example, information learned in one interaction may later help another Copilot feature interpret the same repository.
There are important scope limits. Repository-level facts can only be used in operations on the same repository and repository owners can review and delete them. GitHub also states that stored facts or preferences that go unused are automatically deleted after 28 days, although the timer can reset when an entry is successfully validated and used again.
Governance: enabling, reviewing, and deleting memories
Copilot Memory is in public preview. For organization- or enterprise-managed Copilot subscriptions, the current documentation says the feature is disabled by default until an administrator enables the policy. After that, users can disable it in their own settings. Administrators and repository owners also have controls to review and delete stored repository-level facts.
This matters to security teams because reused context becomes part of the environment that can influence later suggestions. A practical approach is to treat memory curation as part of Copilot governance: remove inaccurate or outdated facts and keep explicit instructions for requirements that should not depend only on automatic inference.
How teams can adapt the review process
The integration does not remove traditional secure code review steps. It changes the source of some of the context used to generate a patch. Teams adopting agentic autofix can therefore add three questions to the review checklist: which convention appears to have guided this fix, is that convention still valid for this code path, and is there any Copilot Memory fact that should be corrected or deleted?
It is also useful to distinguish memory from normative instructions. GitHub presents Copilot Memory as knowledge learned over time, while custom instructions remain the explicit mechanism for rules a team wants Copilot to follow. For critical controls, security requirements, and mandatory architecture decisions, versioned and reviewable instructions are a clearer reference than relying only on what the agent has learned.
What remains open during public preview
Both agentic autofix and Copilot Memory remain in public preview and may change. The September 25 update confirms the integration and reuse of fix patterns, but it does not turn each memory into a guaranteed security rule. Its practical value is to provide more context to the agent, while the decision about whether a fix is appropriate still belongs in the team's review and merge process.