Category

Security for Developers

Secure development, authentication, permissions, dependencies, secrets, OWASP, vulnerabilities and application protection.

13articles
Desenvolvedor diante de um monitor de código com três painéis superiores identificados como CORS, CSRF e CSP, cada um com ícones que representam comunicação entre navegadores, requisição maliciosa e proteção de recursos web.
Security for Developers28/09/20269 min read

CORS, CSRF, and CSP: how to tell three different web security problems apart

CORS, CSRF, and CSP often appear together during debugging, but they address different problems. Learn the difference between origin policy, request forgery, and content policy wit...

Read article

Notebook em uma mesa de desenvolvimento com editor de código, caixas luminosas representando projetos isolados e painel lateral de permissões de sandbox.
Security for Developers27/09/20267 min read

Copilot App gets local sandboxing: how to enable it and review permissions per project

GitHub Copilot app local sandboxing limits file, network, and credential access per project. Learn how to enable, test, and review a least-privilege policy.

Read article
Capa tecnológica em tons azuis com painéis de análise de código exibindo CodeQL 2.27.1, C/C++, C# e Kotlin, gráficos e um escudo digital.
Security for Developers27/09/20267 min read

CodeQL 2.27.1: what changes in C/C++, C#, and Kotlin analysis

Version 2.27.1 adds a C/C++ query, a C# code-quality recommendation, new flow models, and Kotlin 2.4.20 support. See which changes can affect results depending on the active query ...

Read article
Notebook com interface escura inspirada no GitHub Actions mostrando a área de artefatos e ícones visuais de expiração e ocultação.
Security for Developers26/09/20265 min read

GitHub Actions hides expired artifacts: what changes in the UI and API

As of September 24, 2026, expired artifacts no longer appear in the run summary and in REST endpoints named by GitHub. See the impact on integrations, history, retention, and billi...

Read article
Desenvolvedor analisa em uma tela escura um diff de código gerado por IA, com painéis de memória e contexto conectados ao fluxo de revisão de segurança.
Security for Developers26/09/20265 min read

Agentic autofix uses Copilot Memory: what changes in fix review

The integration lets agentic autofix consult existing memories and store fix patterns. See what this changes when reviewing security pull requests.

Read article
Notebook com interface do GitHub exibindo solicitação de reautenticação, ao lado de smartphone com aprovação e ícones de segurança.
Security for Developers25/09/20263 min read

GitHub Proof of Presence: who can enable it and which actions require reauthentication

The preview control adds a Microsoft Entra ID challenge before sensitive actions and uses the same two-hour protected session window as sudo mode.

Read article
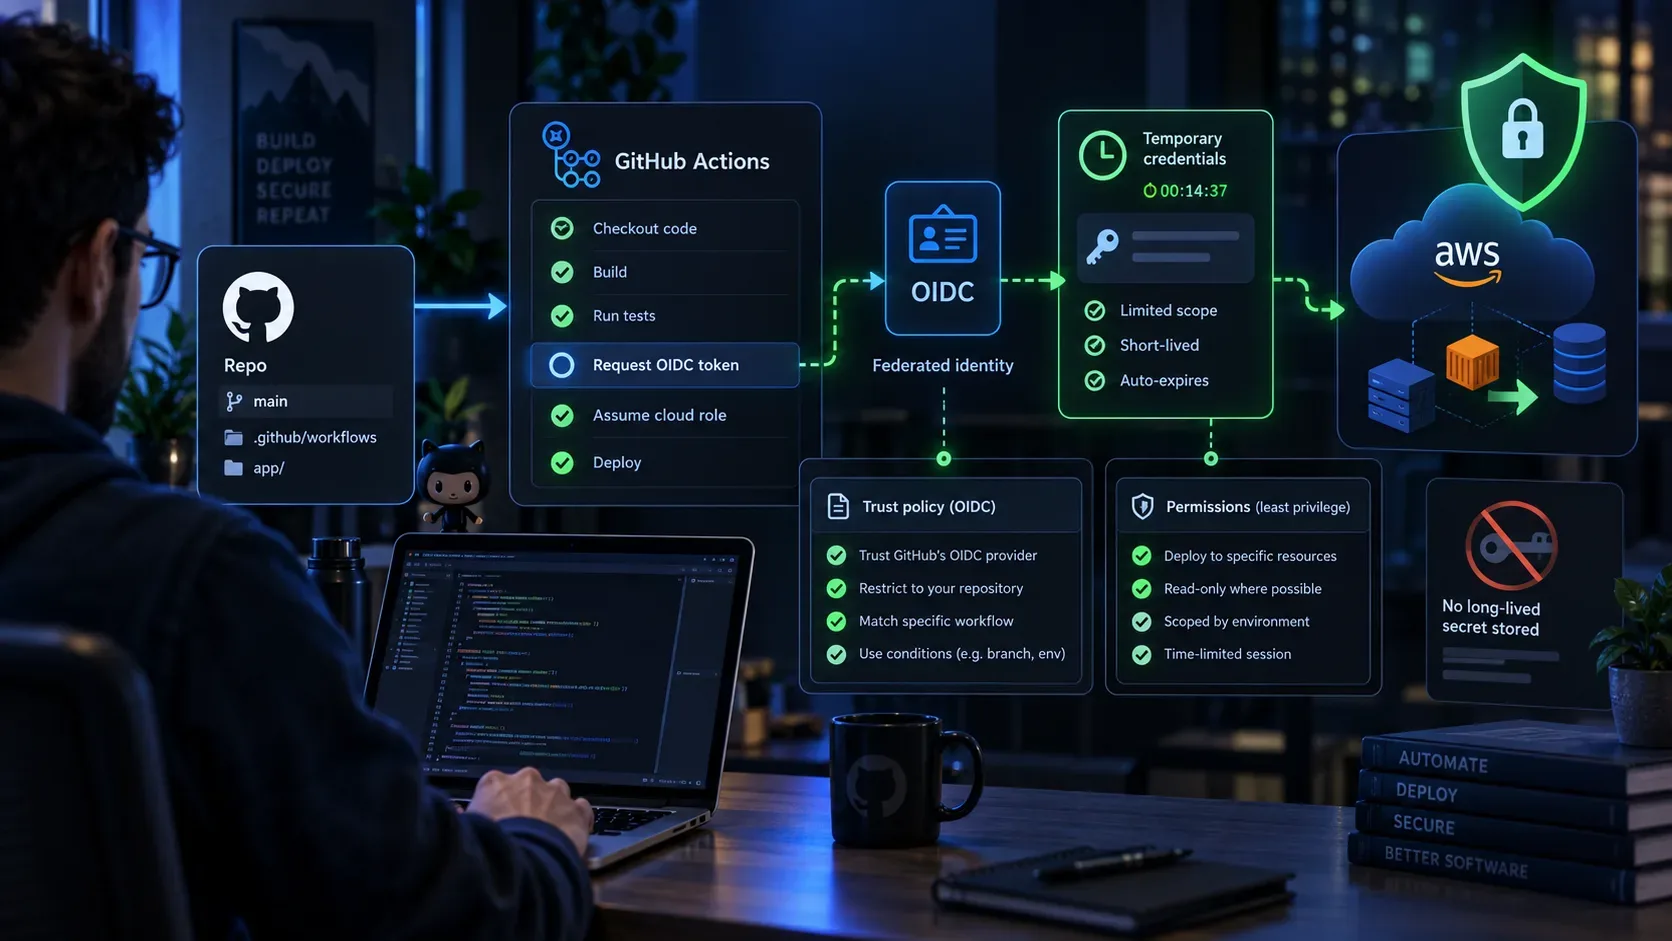
Desenvolvedor diante de um fluxo visual de GitHub Actions com OIDC, credenciais temporárias, controles de permissão e implantação em nuvem.
Security for Developers22/09/20268 min read

GitHub Actions with OIDC: deploy without storing a permanent key in secrets

Learn how to configure OIDC trust, limit permissions, obtain temporary credentials, and test denials in GitHub Actions deployments.

Read article
Notebook em ambiente escuro exibindo revisão de pull request e varredura de segurança por IA, com painéis de organização, API e repositório ao fundo.
Security for Developers11/09/20266 min read

GitHub AI Scan for PRs: how to enable it by API and understand preview limits

Learn how to enable pull request AI Scan by API at the organization and repository levels, which permissions and prerequisites apply, and where the public preview is still limited.

Read article
Desenvolvedor diante de um monitor com YAML e diagrama de CI/CD mostrando cache protegido por cadeado, acessos de leitura e escrita e workflows conectados.
Security for Developers11/09/20267 min read

GitHub Actions cache-mode: least privilege without breaking caches or reusable workflows

Learn when to use read, write, write-only, and none, how defaults change by trigger, and how to cap reusable workflows without losing cache performance.

Read article
Estação de trabalho azul com laptop exibindo um workflow do GitHub Actions, bloco de permissões do GITHUB_TOKEN e alertas de vulnerabilidade do Dependabot.
Security for Developers10/09/20268 min read

GitHub Actions: how to use vulnerability-alerts to read Dependabot alerts with least privilege

Learn how to use vulnerability-alerts: read on GITHUB_TOKEN to query Dependabot alerts with minimal access, including YAML, API, forks, and reusable workflows.

Read article
Smartphone exibindo um escudo do Android acima de um chip StrongBox, cercado por cartões de identificação e um cadeado metálico.
Security for Developers06/09/20268 min read

Android and StrongBox: how hardware supports high-assurance digital credentials

Learn where StrongBox fits in Android's chain of trust, what the hardware actually guarantees, and which limits matter to developers.

Read article
Smartphone com interface genérica de publicação de app, escudo com marca de verificação, checklist e mapa luminoso do Brasil ao fundo.
Security for Developers02/09/20267 min read

Android developer verification on Sept. 30, 2026: what changes in Brazil and a checklist to keep apps registered

Learn which installations fall under the September 30 rule, how Play differs from external distribution, and what to review before the deadline.

Read article